
199 lines
10 KiB
JSON
199 lines
10 KiB
JSON
{
|
|
"dataType": "CVE_RECORD",
|
|
"dataVersion": "5.1",
|
|
"cveMetadata": {
|
|
"cveId": "CVE-2024-26152",
|
|
"assignerOrgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
|
|
"state": "PUBLISHED",
|
|
"assignerShortName": "GitHub_M",
|
|
"dateReserved": "2024-02-14T17:40:03.690Z",
|
|
"datePublished": "2024-02-22T21:52:26.193Z",
|
|
"dateUpdated": "2024-08-14T15:32:05.054Z"
|
|
},
|
|
"containers": {
|
|
"cna": {
|
|
"title": "Label Studio vulnerable to Cross-site Scripting if `<Choices>` or `<Labels>` are used in labeling config ",
|
|
"problemTypes": [
|
|
{
|
|
"descriptions": [
|
|
{
|
|
"cweId": "CWE-79",
|
|
"lang": "en",
|
|
"description": "CWE-79: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')",
|
|
"type": "CWE"
|
|
}
|
|
]
|
|
}
|
|
],
|
|
"metrics": [
|
|
{
|
|
"cvssV3_1": {
|
|
"attackComplexity": "LOW",
|
|
"attackVector": "NETWORK",
|
|
"availabilityImpact": "NONE",
|
|
"baseScore": 4.7,
|
|
"baseSeverity": "MEDIUM",
|
|
"confidentialityImpact": "LOW",
|
|
"integrityImpact": "NONE",
|
|
"privilegesRequired": "NONE",
|
|
"scope": "CHANGED",
|
|
"userInteraction": "REQUIRED",
|
|
"vectorString": "CVSS:3.1/AV:N/AC:L/PR:N/UI:R/S:C/C:L/I:N/A:N",
|
|
"version": "3.1"
|
|
}
|
|
}
|
|
],
|
|
"references": [
|
|
{
|
|
"name": "https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg",
|
|
"tags": [
|
|
"x_refsource_CONFIRM"
|
|
],
|
|
"url": "https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg"
|
|
},
|
|
{
|
|
"name": "https://github.com/HumanSignal/label-studio/pull/5232",
|
|
"tags": [
|
|
"x_refsource_MISC"
|
|
],
|
|
"url": "https://github.com/HumanSignal/label-studio/pull/5232"
|
|
},
|
|
{
|
|
"name": "https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8",
|
|
"tags": [
|
|
"x_refsource_MISC"
|
|
],
|
|
"url": "https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8"
|
|
},
|
|
{
|
|
"name": "https://github.com/HumanSignal/label-studio/releases/tag/1.11.0",
|
|
"tags": [
|
|
"x_refsource_MISC"
|
|
],
|
|
"url": "https://github.com/HumanSignal/label-studio/releases/tag/1.11.0"
|
|
}
|
|
],
|
|
"affected": [
|
|
{
|
|
"vendor": "HumanSignal",
|
|
"product": "label-studio",
|
|
"versions": [
|
|
{
|
|
"version": "< 1.11.0",
|
|
"status": "affected"
|
|
}
|
|
]
|
|
}
|
|
],
|
|
"providerMetadata": {
|
|
"orgId": "a0819718-46f1-4df5-94e2-005712e83aaa",
|
|
"shortName": "GitHub_M",
|
|
"dateUpdated": "2024-02-22T21:52:26.193Z"
|
|
},
|
|
"descriptions": [
|
|
{
|
|
"lang": "en",
|
|
"value": "### Summary\nOn all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability.\n\n### Details\nNeed permission to use the \"data import\" function. This was reproduced on Label Studio 1.10.1.\n\n### PoC\n\n1. Create a project.\n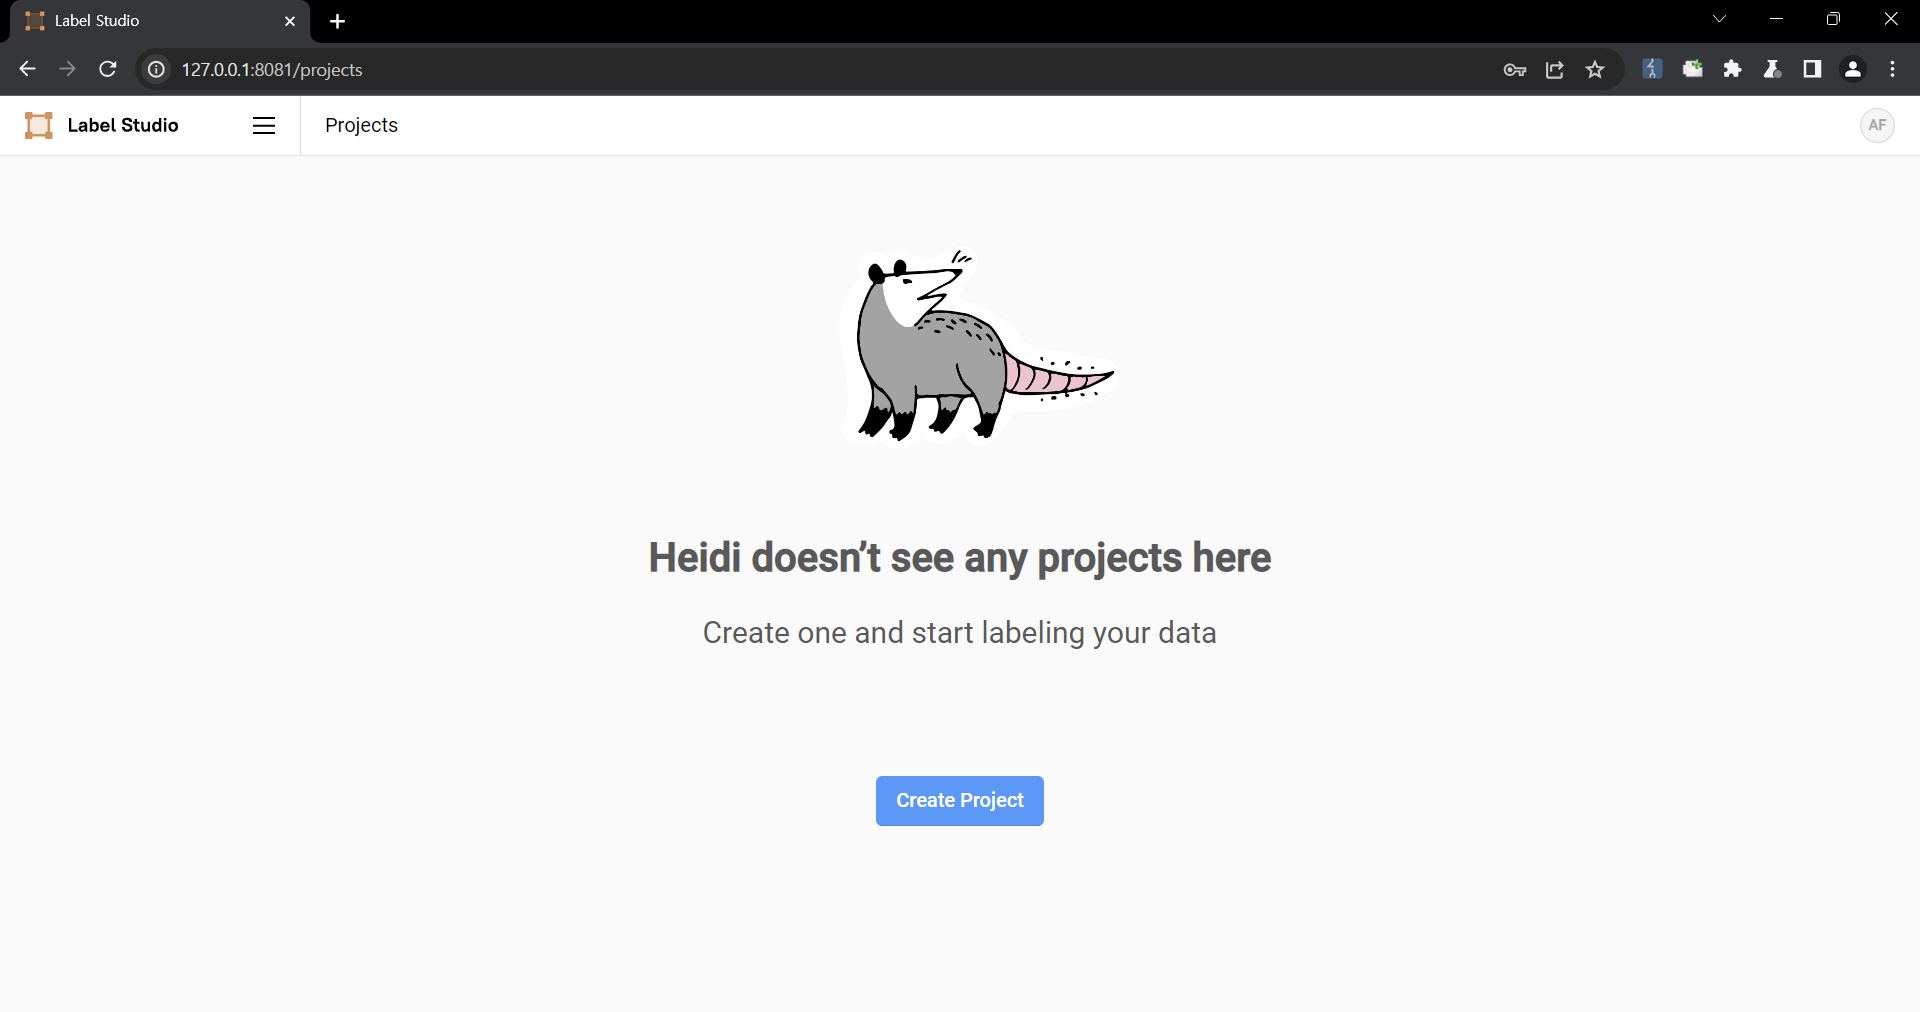\n\n2. Upload a file containing the payload using the \"Upload Files\" function.\n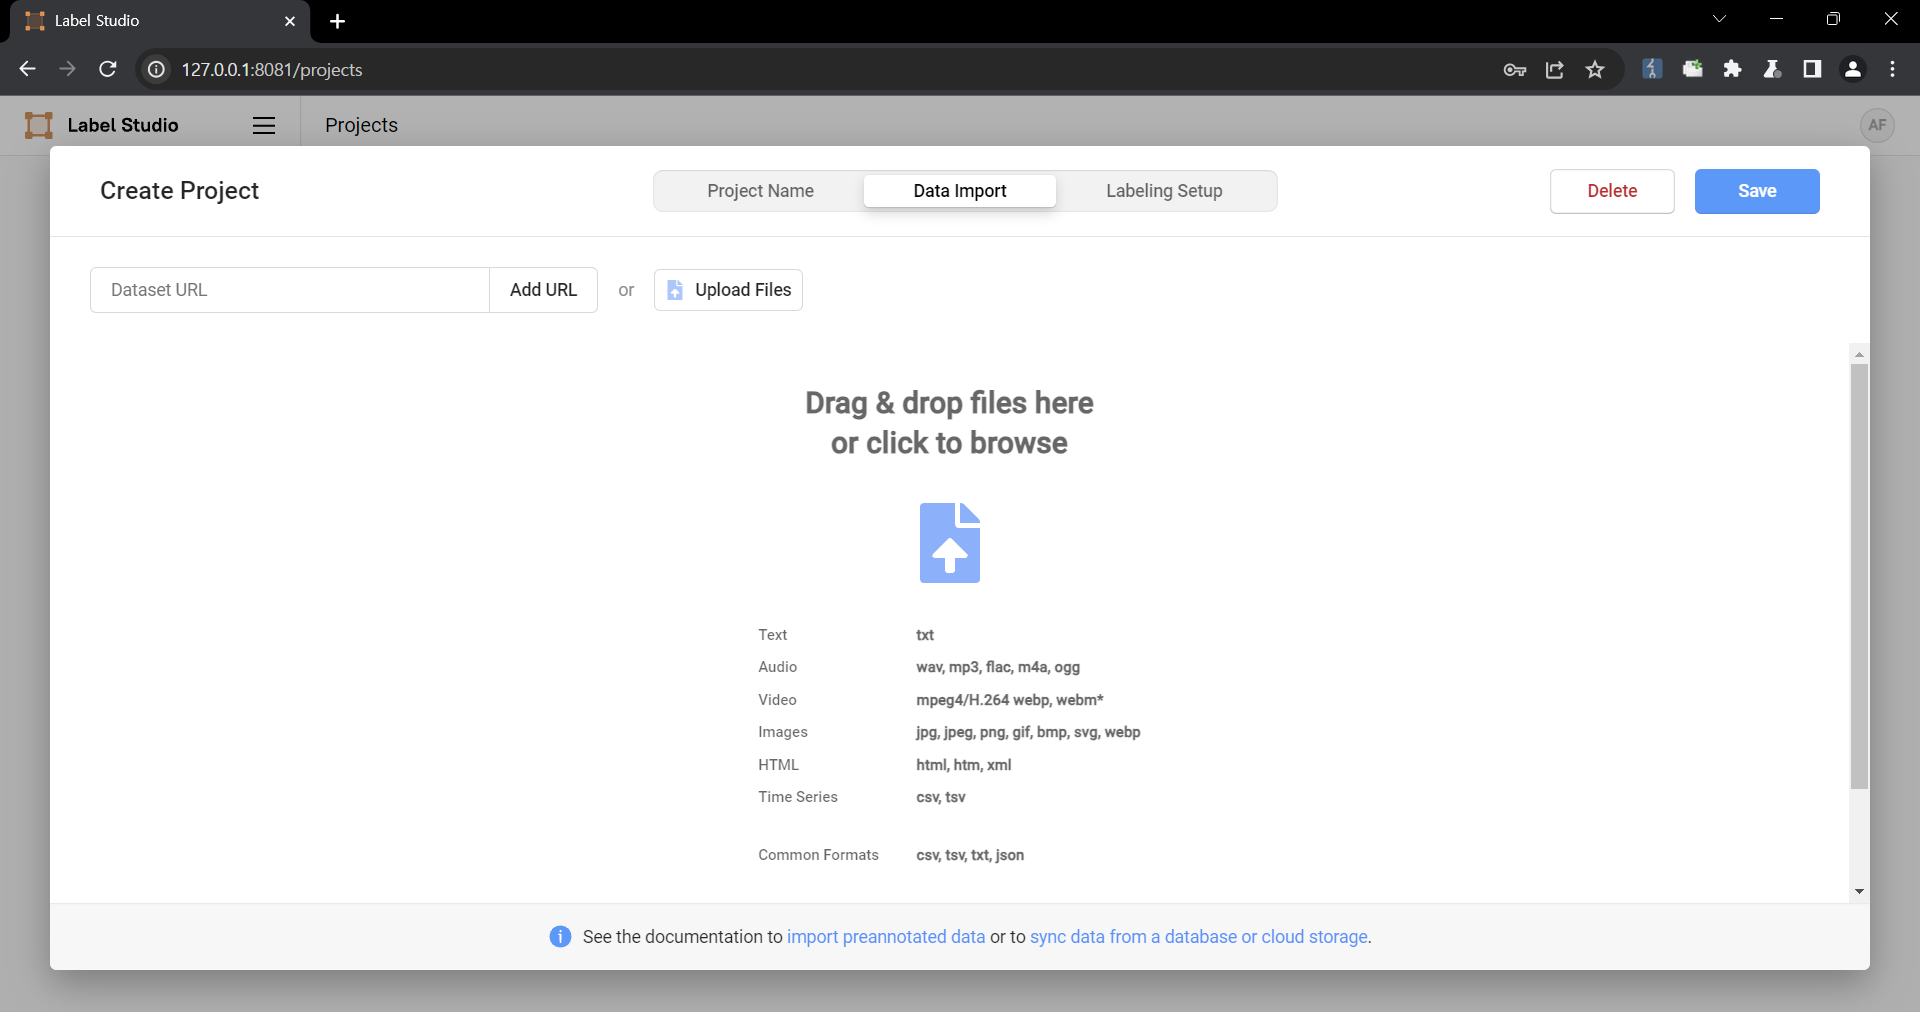\n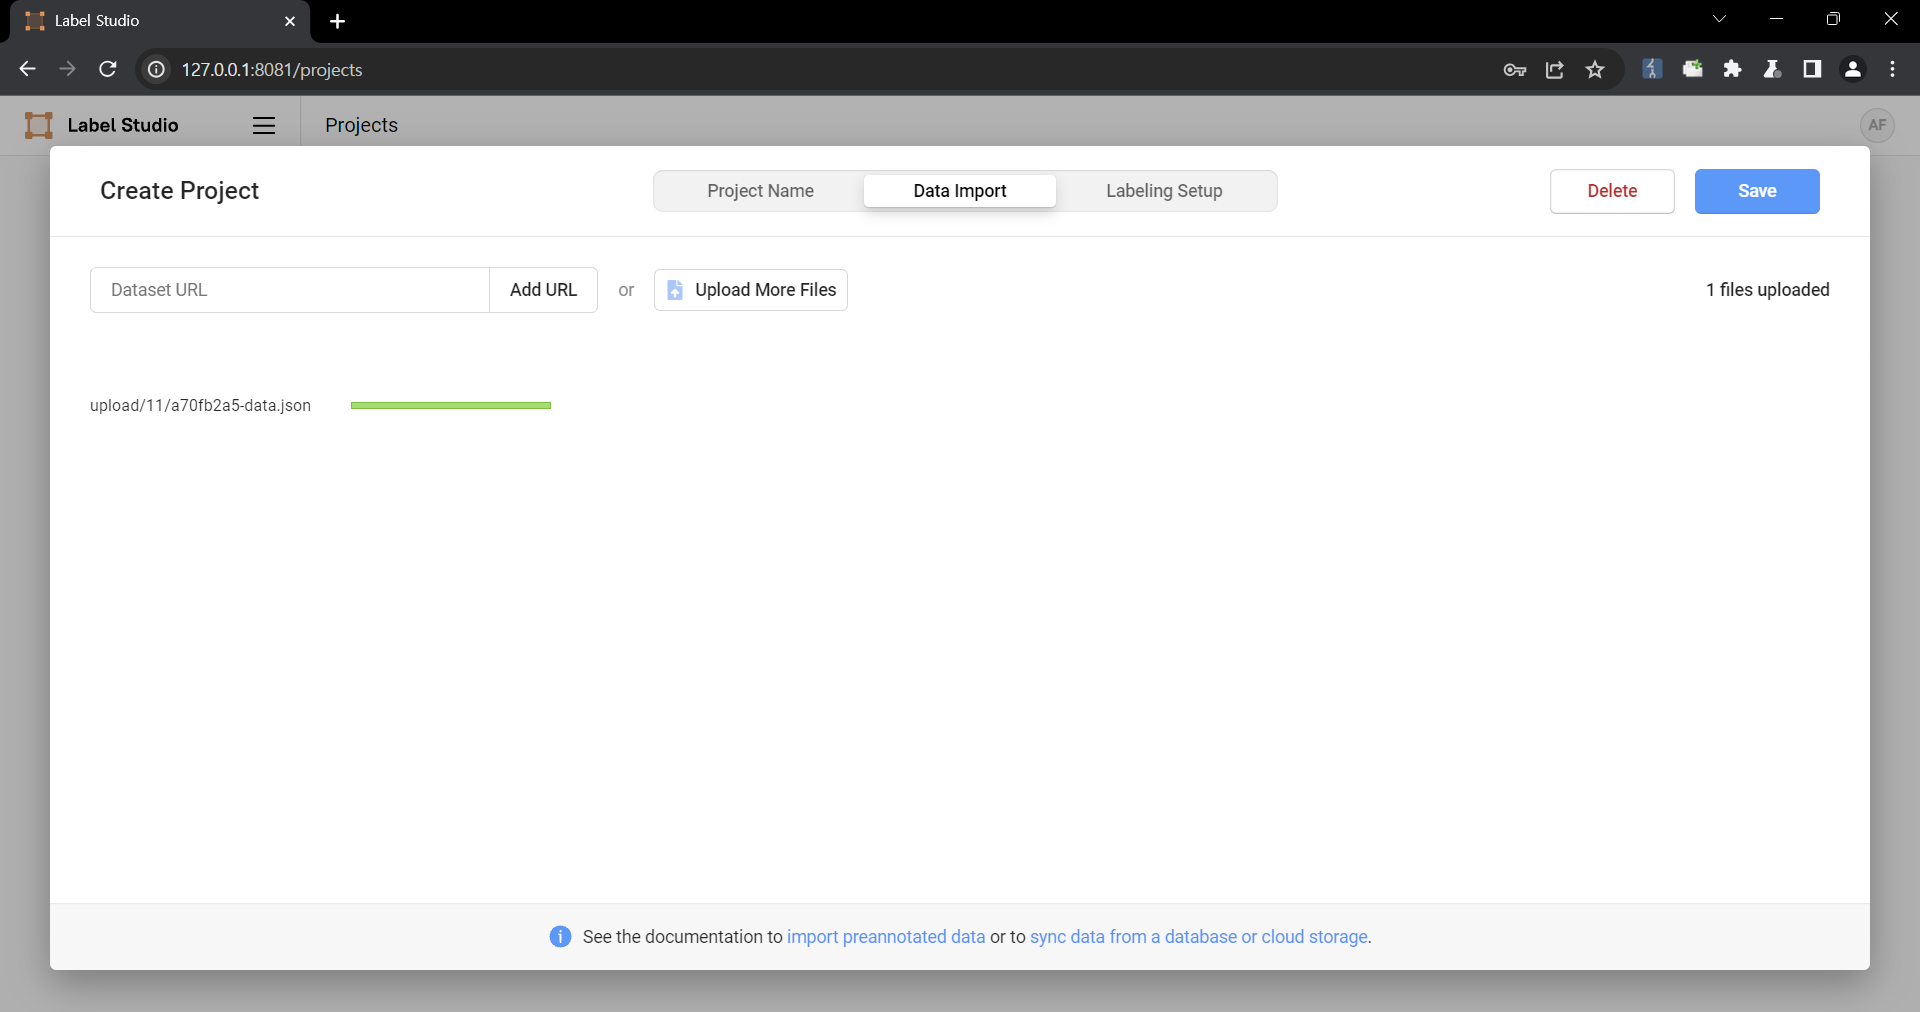\n\nThe following are the contents of the files used in the PoC\n```\n{\n \"data\": {\n \"prompt\": \"labelstudio universe image\",\n \"images\": [\n {\n \"value\": \"id123#0\",\n \"style\": \"margin: 5px\",\n \"html\": \"<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_ZaBSvC.avif' onload=alert(document.cookie)>\"\n }\n ]\n }\n}\n```\n\n3. Select the text-to-image generation labeling template of Ranking and scoring\n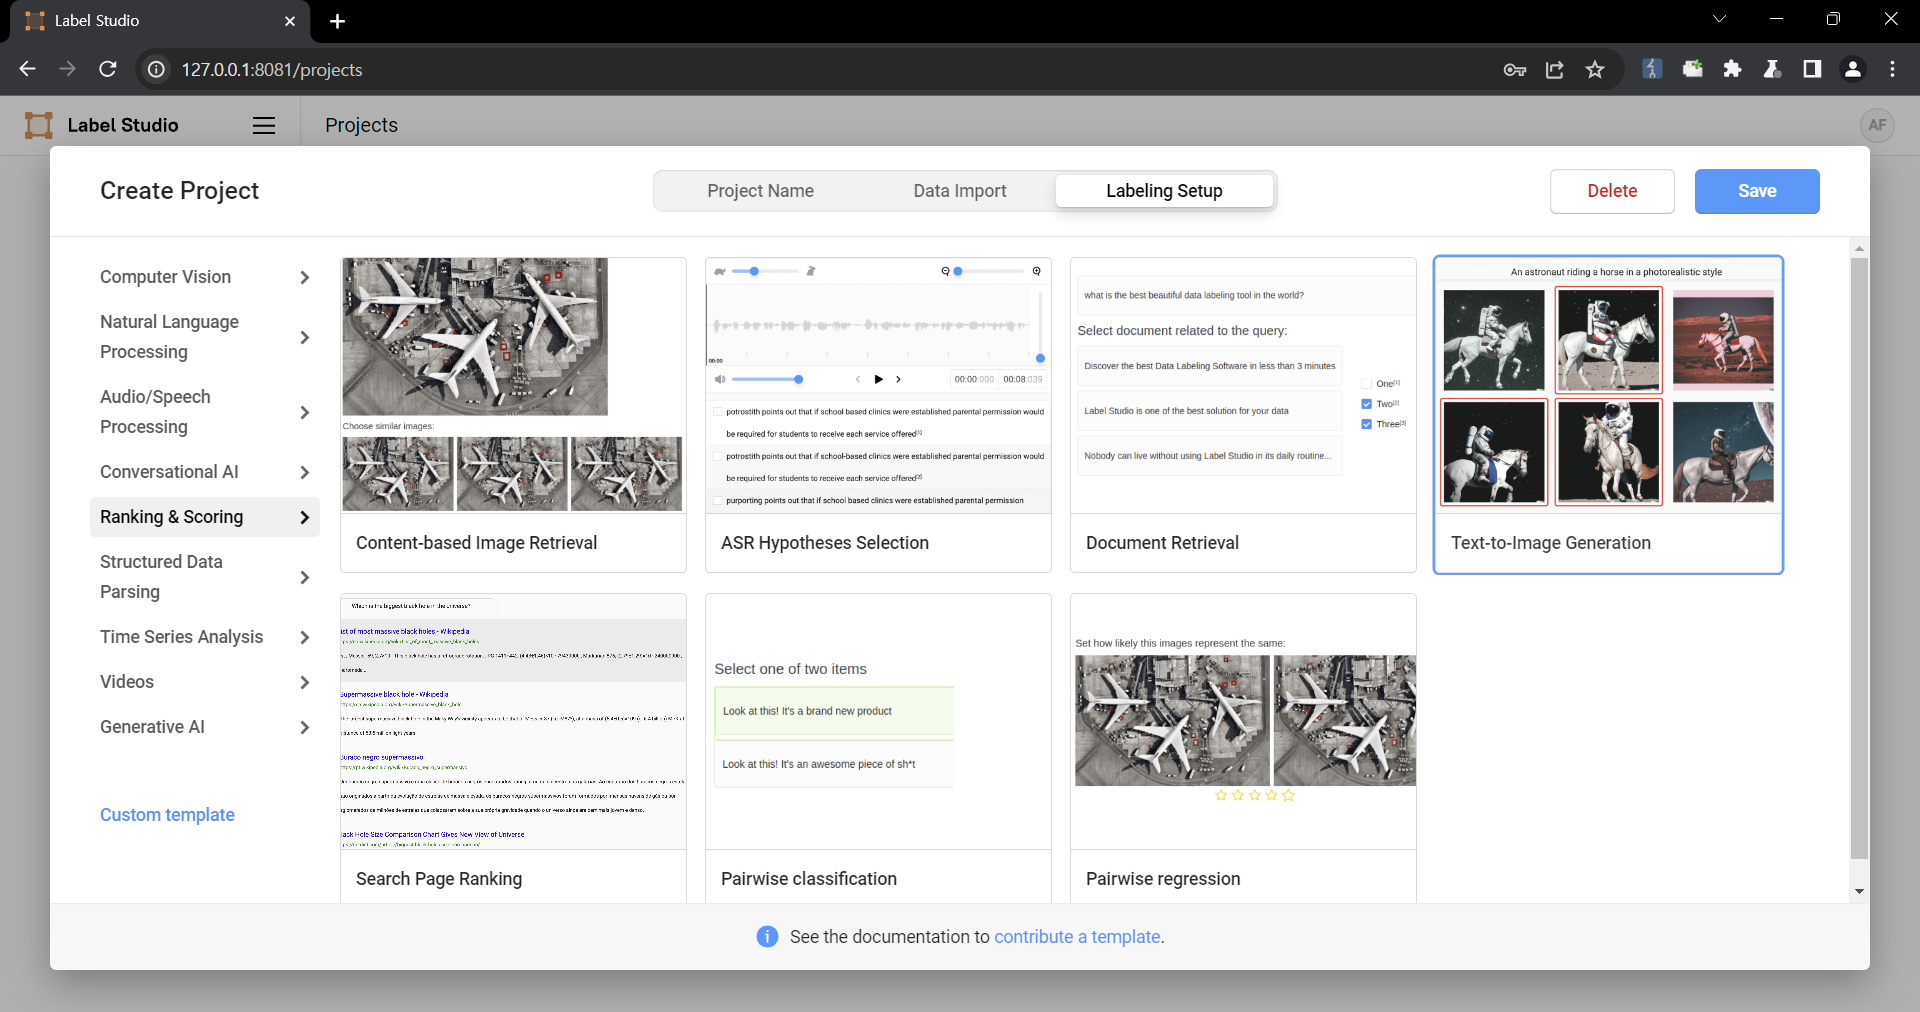\n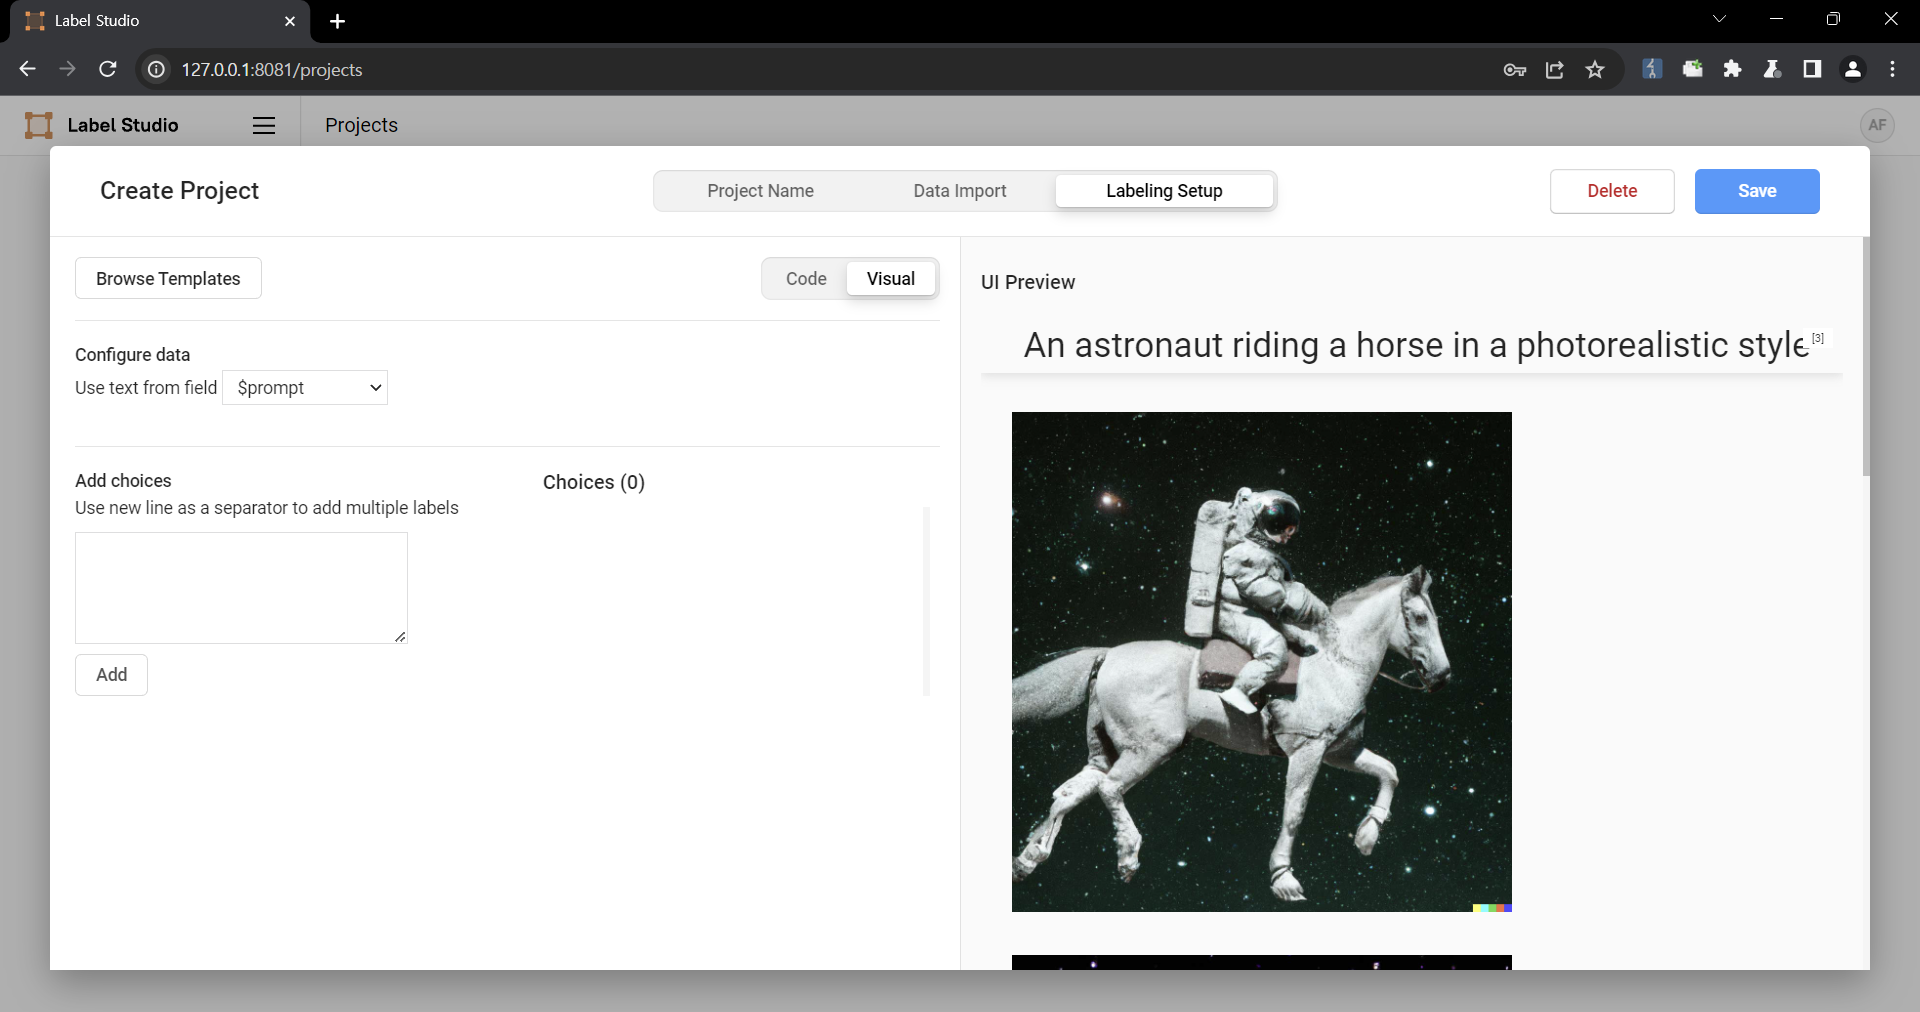\n\n4. Select a task\n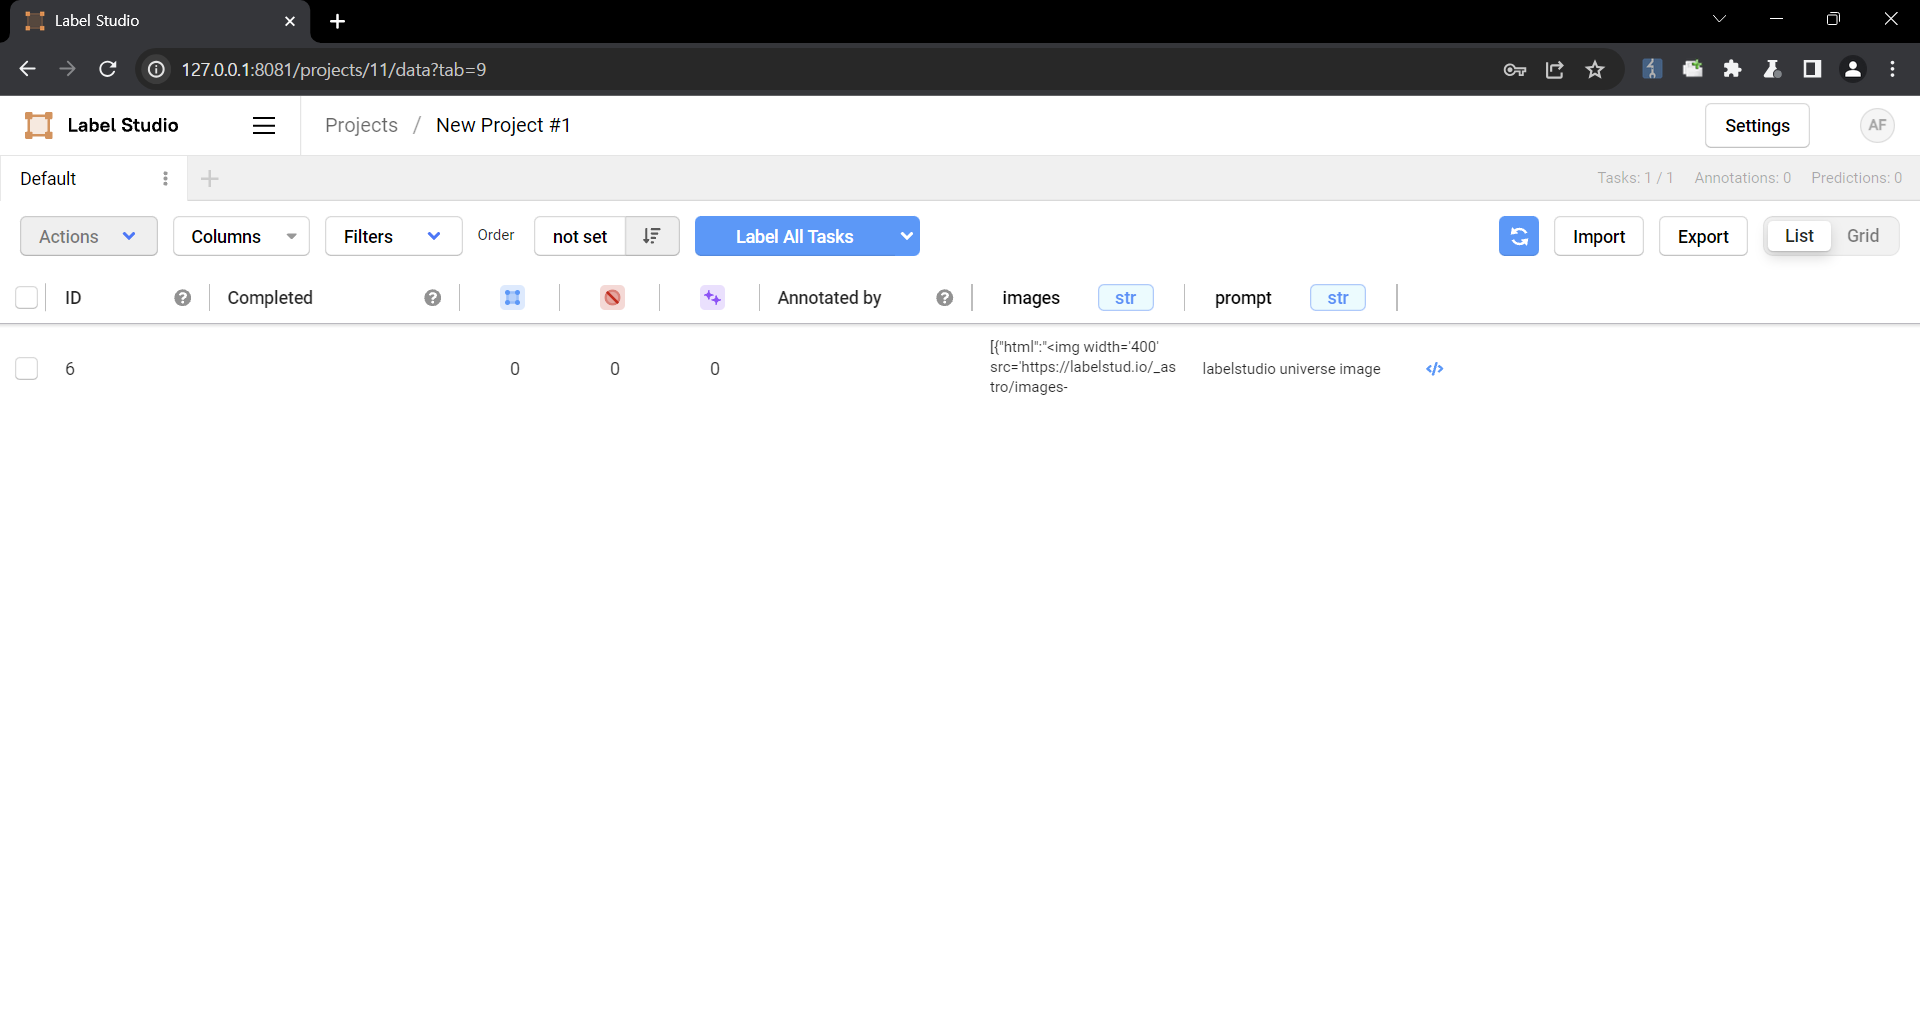\n\n5. Check that the script is running\n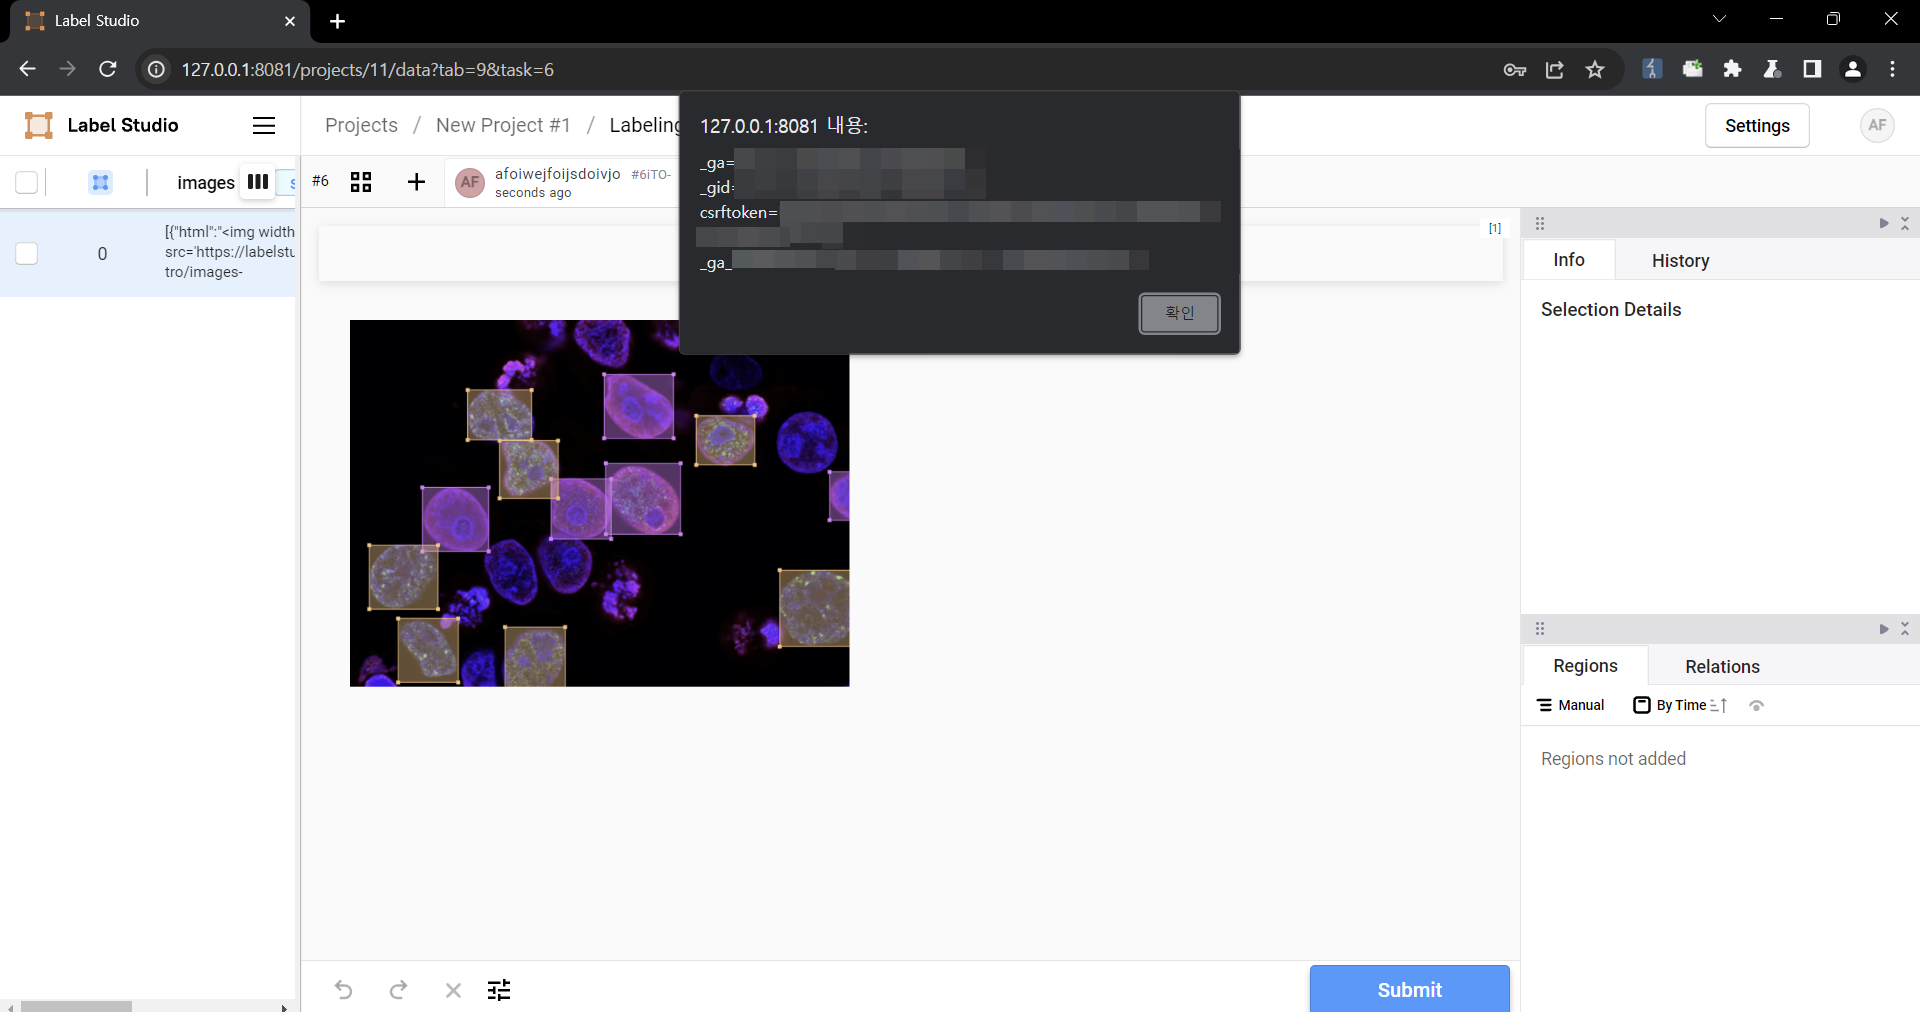\n\n### Impact\nMalicious scripts can be injected into the code, and when linked with vulnerabilities such as CSRF, it can cause even greater damage. In particular, It can become a source of further attacks, especially when linked to social engineering.\n"
|
|
}
|
|
],
|
|
"source": {
|
|
"advisory": "GHSA-6xv9-957j-qfhg",
|
|
"discovery": "UNKNOWN"
|
|
}
|
|
},
|
|
"adp": [
|
|
{
|
|
"providerMetadata": {
|
|
"orgId": "af854a3a-2127-422b-91ae-364da2661108",
|
|
"shortName": "CVE",
|
|
"dateUpdated": "2024-08-01T23:59:32.696Z"
|
|
},
|
|
"title": "CVE Program Container",
|
|
"references": [
|
|
{
|
|
"name": "https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg",
|
|
"tags": [
|
|
"x_refsource_CONFIRM",
|
|
"x_transferred"
|
|
],
|
|
"url": "https://github.com/HumanSignal/label-studio/security/advisories/GHSA-6xv9-957j-qfhg"
|
|
},
|
|
{
|
|
"name": "https://github.com/HumanSignal/label-studio/pull/5232",
|
|
"tags": [
|
|
"x_refsource_MISC",
|
|
"x_transferred"
|
|
],
|
|
"url": "https://github.com/HumanSignal/label-studio/pull/5232"
|
|
},
|
|
{
|
|
"name": "https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8",
|
|
"tags": [
|
|
"x_refsource_MISC",
|
|
"x_transferred"
|
|
],
|
|
"url": "https://github.com/HumanSignal/label-studio/commit/5df9ae3828b98652e9fa290a19f4deedf51ef6c8"
|
|
},
|
|
{
|
|
"name": "https://github.com/HumanSignal/label-studio/releases/tag/1.11.0",
|
|
"tags": [
|
|
"x_refsource_MISC",
|
|
"x_transferred"
|
|
],
|
|
"url": "https://github.com/HumanSignal/label-studio/releases/tag/1.11.0"
|
|
}
|
|
]
|
|
},
|
|
{
|
|
"affected": [
|
|
{
|
|
"vendor": "humansignal",
|
|
"product": "label_studio",
|
|
"cpes": [
|
|
"cpe:2.3:a:humansignal:label_studio:*:*:*:*:*:*:*:*"
|
|
],
|
|
"defaultStatus": "unknown",
|
|
"versions": [
|
|
{
|
|
"version": "0",
|
|
"status": "affected",
|
|
"lessThan": "1.11.0",
|
|
"versionType": "custom"
|
|
}
|
|
]
|
|
}
|
|
],
|
|
"metrics": [
|
|
{
|
|
"other": {
|
|
"type": "ssvc",
|
|
"content": {
|
|
"timestamp": "2024-02-23T14:32:49.819252Z",
|
|
"id": "CVE-2024-26152",
|
|
"options": [
|
|
{
|
|
"Exploitation": "poc"
|
|
},
|
|
{
|
|
"Automatable": "no"
|
|
},
|
|
{
|
|
"Technical Impact": "partial"
|
|
}
|
|
],
|
|
"role": "CISA Coordinator",
|
|
"version": "2.0.3"
|
|
}
|
|
}
|
|
}
|
|
],
|
|
"title": "CISA ADP Vulnrichment",
|
|
"providerMetadata": {
|
|
"orgId": "134c704f-9b21-4f2e-91b3-4a467353bcc0",
|
|
"shortName": "CISA-ADP",
|
|
"dateUpdated": "2024-08-14T15:32:05.054Z"
|
|
}
|
|
}
|
|
]
|
|
}
|
|
} |